
Share


Splynx pairs carrier-grade AAA with ISP RADIUS billing software to automate authentication and revenue workflows end-to-end.
Splynx consists of several sub-systems. One of its leading and most essential parts is the Splynx RADIUS server: PPPoE, DHCP, IPoE, Hotspot or Wireless authentication. Customers with static IPs are managed too, via the MikroTik API (see below). You don’t deploy or maintain a separate RADIUS server: FreeRADIUS ships with Splynx, bundled, pre-configured and connected to your customer data. Splynx also provides smart bandwidth management, billing, network management and other useful features.
The Splynx RADIUS server is used to perform AAA tasks:
The Splynx RADIUS server has two parts: FreeRADIUS, which receives requests from your routers, and Splynx, which checks each request against your customer data: whether the customer exists, whether their service is active, and which speed their plan gives. You control the answers from Splynx settings: the attributes sent for each router type (NAS type), extra attributes per customer or per plan, blocking methods and FUP rules.
A typical connection looks like this:
Each vendor uses its own rate-limit format: Mikrotik-Rate-Limit for MikroTik, WISPr-Bandwidth-Max-Down for Ubiquiti, Cisco-Avpair rate-limit for Cisco. These attributes are pre-configured per NAS type, so you pick your vendor under Config → Networking → Radius, click Load and adjust only what you need. Because Splynx uses FreeRADIUS, its attribute dictionaries cover most common device manufacturers; if you need a dictionary for a specific device, our support team can help install it.
With Splynx you can set up administrator access to equipment to check their credentials over the RADIUS server database.
If their username/password is correct, they will be able to log in to the equipment. If not, they will not get access. This is a very convenient approach compared to local login.
Imagine you hire a new administrator and, in one case, you need to update hundreds of routers, APs, and switches to create a local login everywhere. In another case, you give a new hire one common login/password but must remember to change those credentials when a person leaves the company.
The best-case scenario is to connect all networking devices to the RADIUS server and verify administrator login using RADIUS protocol.
Authorization means that different levels of access can be implemented. Some administrators can change the configurations. Some can only view and read config.
Splynx stores information on when the network unit was accessed by an administrator: for MikroTik routers, every login and logout is logged under Administration → Logs → Operations.
Check out the tutorials on how to configure admin login using the Splynx RADIUS server on different platforms:
Splynx supports different ways of central customer authentication in a broadband network. The choice depends on the network topology and the technology the operator decides to use. The most widely used access technologies, with their advantages and disadvantages, are described below:
RADIUS follows each customer’s status in Splynx, so it also handles blocking, for example of non-payers. You choose the method per NAS type:
Reject_1 address list. The session isn’t interrupted, so you can still give the customer access to local resources without changing their IP address.Fair usage policy (FUP) rules use the same mechanism: Splynx sends a CoA request with the FUP rate-limit or block attributes set for the NAS type. More on this in our post on blocking non-paying customers in Splynx. To show blocked customers why they’re blocked and let them pay right away, Splynx can also redirect them to a landing page via DNS: see redirecting blocked customers to a payment page.
If routers can’t reach RADIUS, new sessions can’t be authorized. Two options keep customers connecting:
To keep accounting data on a second server as well, use proxy accounting: Splynx copies RADIUS accounting packets to another RADIUS server. Setup is in the knowledge base: RADIUS proxy accounting.
The guides below show how to set up customer authentication on different equipment. If you run MikroTik, start with our post on MikroTik RADIUS configuration and troubleshooting; if your router gets no answer from RADIUS, see RADIUS server network issues. For per-device Wi-Fi passwords on one SSID, see Multiple PSK, which you enable in the RADIUS advanced settings.
Check out these manuals for different types of user authentication in Splynx:
2. MikroTik: PPPoE and other PPP tunnels with RADIUS
3. MikroTik: Hotspot with RADIUS
4. MikroTik: OpenVPN with RADIUS
5. MikroTik: Static IP addressing with API authentication/accounting
6. MikroTik: Local DHCP with MikroTik API
7. Ubiquiti: Wireless authentication with RADIUS
8. Ubiquiti: PPPoE authentication on EdgeRouters
9. Cisco IOS: PPPoE with RADIUS
10. Cambium: Wireless authentication via RADIUS
11. Juniper: PPPoE with RADIUS
12. Cisco IOS XE: PPPoE with RADIUS
13. Cisco ASR 9010: PPPoE with RADIUS
14. netElastic vBNG: PPPoE with RADIUS
15. netElastic vBNG: IPoE with RADIUS
17. Linux: Accel-PPP server with IPoE
18. MikroTik: Wireless ACL authentication
19. DHCP Option 82
MDU Wi-Fi onboarding: let residents sign up, pay, and connect on their own
Give every apartment a QR card and let residents sign up, pay, and get a private Wi-Fi password on a shared SSID, withou...
What is mPSK? Multiple PSK for simple per-device control of Wi-Fi networks
mPSK support is part of Splynx, so you can easily segment your WiFi Network with Private Pre-Shared-Keys without requiri...
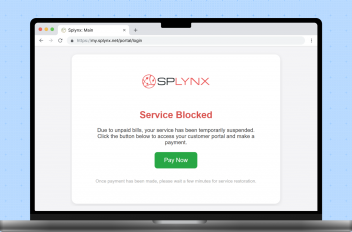
Improve Non-Payment Handling with Splynx DNS Blocking
Tackle non-payments more proficiently by redirecting blocked customers to a landing page. From there, they can easily ac...
Switch to the safe side and let network engineers sleep well at night
Running a local ISP comes with enough challenges — worrying about network failures and blocking non-paying customers d...
Using TR-069 ACS to Deliver High-Quality Wi-Fi to Residential Customers While Cutting Costs
TR-069 ACS isn't a magic pill for all troubles, but it can make your life much easier. This article we'll guide you thro...

Bufferbloat explained: why bandwidth isn’t the key to QoE for ISPs
Bufferbloat is lag that appears when a link is busy: oversized buffers fill up and every packet waits. More bandwidth wo...
Simplifying Network Management for ISPs with Splynx Network Sites
Splynx Network sites bring ISPs around the world more streamlined client communication and efficient tracking for all yo...
Simplifying network troubleshooting with Ping and Traceroute features
Explore Splynx 4.2's Ping and Traceroute features, simplifying network troubleshooting and boosting ISP team efficiency.
Hardware Backup & Change Management in Splynx
Maintaining network stability and reliability is paramount for both ISPs and their valued customers. To address this, Sp...
Bandwidth management in Splynx
As a local ISP business owner, ensuring efficient bandwidth management is crucial for maintaining customer satisfaction ...
Find out how Splynx helps ISPs grow
Learn more


