
Share


RouterOS 7 has no IP accounting. If you need traffic statistics from a MikroTik router, you get them from Traffic Flow, MikroTik’s NetFlow-compatible exporter. The router keeps track of the flows passing through it and sends flow records over UDP to an external collector, which stores and analyzes them.
This guide covers what Traffic Flow exports, which NetFlow version to pick, the RouterOS 7 commands, the traps that make counters look wrong, and how to send the flows to Splynx for subscriber usage accounting.
NetFlow is Cisco’s format for exporting statistics about the flows of packets that pass through a router. Each flow record describes one flow: its addresses, ports and protocol, its timing, and how much traffic it carried. A collector gathers the records and turns them into usage statistics and reports.
Traffic Flow is MikroTik’s implementation. In MikroTik’s words, “Traffic-Flow is compatible with Cisco NetFlow, so utilities designed for NetFlow work with it.” Besides monitoring and accounting, MikroTik positions it as a way to find problems in the network and to analyze and optimize its performance.
The router holds active flows in a cache and exports each flow when it expires: after 15 seconds without a new packet, or after 30 minutes even if packets keep coming (the defaults).
MikroTik removed IP accounting starting from RouterOS 7.x. Anything that read the IP accounting table needs another data source after the upgrade to v7.
In Splynx, this concerns API accounting: Splynx logs in to the router through the MikroTik API every 5 minutes and reads the IP Accounting snapshot table. On RouterOS 7, either keep that router on older firmware or switch it to another accounting type, such as NetFlow (below) or RADIUS accounting.
Splynx says the same on the router page (Networking → Routers): if you choose API accounting, a note explains that the option “is only supported on MikroTik RouterOS version lower than 7.x” and asks you to select NetFlow accounting on v7.x.
RouterOS exports four formats:
| Version | What it carries |
|---|---|
| NetFlow v1 | The original format: basic information about IP flows, without support for different protocol types or Type of Service (ToS) |
| NetFlow v5 | Adds ToS, TCP flags and autonomous-system fields. RouterOS does not fill the BGP AS numbers |
| NetFlow v9 | Template-based format with new record types; exports IPv4 and IPv6 flows |
| IPFIX | The IETF standard based on NetFlow v9, with more customizable records and newer fields such as multicast |
Pick the version your collector expects. If you need IPv6 flows, MikroTik names v9 as the format that exports both IPv4 and IPv6. With v9 and IPFIX, the router also sends templates that describe the records. v9-template-refresh resends them every 20 export packets by default; v9-template-timeout sends them after a set time if they haven’t gone out by then.
The commands below use the RouterOS 7 path syntax and come from MikroTik’s Traffic Flow manual. Replace the example addresses with your own.
/ip/traffic-flow/set enabled=yes
/ip/traffic-flow/print
print shows the current settings. After enabling, the output looks like this (all values except enabled are the defaults):
                enabled: yes
             interfaces: all
          cache-entries: 256k
    active-flow-timeout: 30m
  inactive-flow-timeout: 15s
packet-sampling: nointerfaces: the interfaces whose forwarded traffic is accounted, as a comma-separated list or all.cache-entries: how many flow records the router holds in memory at once. The default depends on the device’s memory: 256k on larger boards, down to 4k on the smallest. Allowed values run from 1k to 32M.active-flow-timeout and inactive-flow-timeout: when a flow is expired and exported. MikroTik warns that a very short inactive timeout can create many flows and overflow the buffer.In WinBox, the same settings are under IP → Traffic Flow:
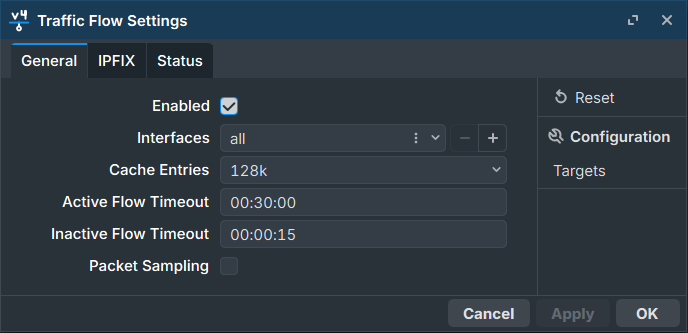
The screenshot uses 128k cache entries, the minimum Splynx recommends for NetFlow accounting.
/ip/traffic-flow/target/add dst-address=192.168.0.2 port=2055 version=9
/ip/traffic-flow/target/printdst-address: the collector’s IP address (the only mandatory field).port: the UDP port the collector listens on. The default is 2055.version: 1, 5, 9 or ipfix.src-address: the source address of the export packets. The default 0.0.0.0 lets the router use the address of the outgoing interface.In WinBox, click Targets in the Traffic Flow Settings window and add the same values.
/ip/traffic-flow/monitor duration=3active-flows should climb as the router routes traffic, and finished-flows should start climbing once flows expire and are exported. If your collector receives nothing, check these counters first, then the target entry, then whether the traffic you’re watching passes through the router’s CPU at all (see the next section).
With IPFIX, you choose which fields go into the records under /ip/traffic-flow/ipfix. All fields are on by default; turn off the ones you don’t need:
/ip/traffic-flow/ipfix/set gateway=no tcp-flags=noPacket sampling accounts for only part of the packets. Here the router samples 2222 packets in a row, skips 1111, and repeats:
/ip/traffic-flow/set packet-sampling=yes sampling-interval=2222 sampling-space=1111With sampling on, the flow totals don’t include every packet, so leave it off when you use the flows for usage accounting.
port to what your collector listens on.src-address=0.0.0.0, the source address depends on the outgoing interface. If your collector identifies routers by IP address, as Splynx does, set src-address explicitly and make sure the export isn’t NATed on the way.cache-entries only as far as the router’s memory allows.Any collector that accepts NetFlow or IPFIX can receive Traffic Flow exports. MikroTik’s own documentation mentions two setups:
On the command line, the nfdump tools collect flows with the nfcapd daemon and query them with nfdump. Splynx uses the same tools internally.
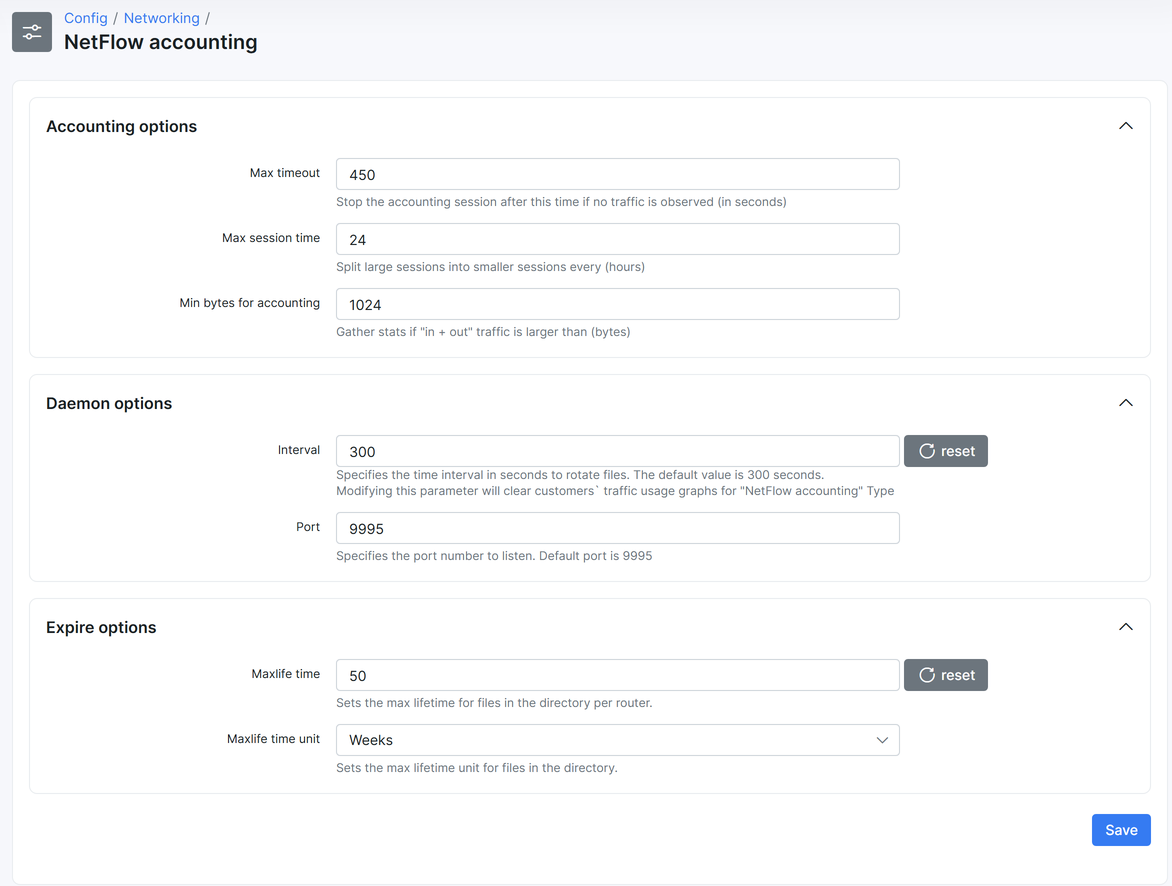
If your broadband business runs Splynx, you don’t need a separate collector for usage accounting. Splynx is a NetFlow collector and analyzer: once you add a router with NetFlow accounting, Splynx receives its flows, counts each customer’s ICMP, UDP and TCP traffic, and marks sessions as online. It listens on UDP port 9995 by default. Splynx also supports NetFlow v9; the setup example in the Splynx documentation uses v5.
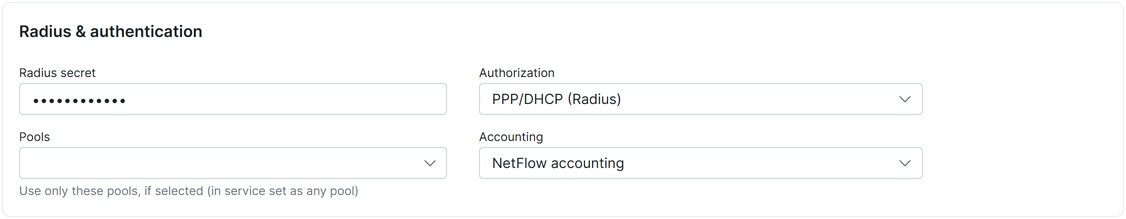
On the router’s page (Networking → Routers), choose NetFlow accounting in the Accounting field. Authorization can stay on RADIUS:
The port and the other collector settings are under Config → Networking → NetFlow accounting:
On the MikroTik side, the documented example uses v5. Here Splynx is at 10.250.32.1 and the router at 10.250.32.5:
/ip/traffic-flow/set enabled=yes cache-entries=128k
/ip/traffic-flow/target/add dst-address=10.250.32.1 src-address=10.250.32.5 port=9995 version=5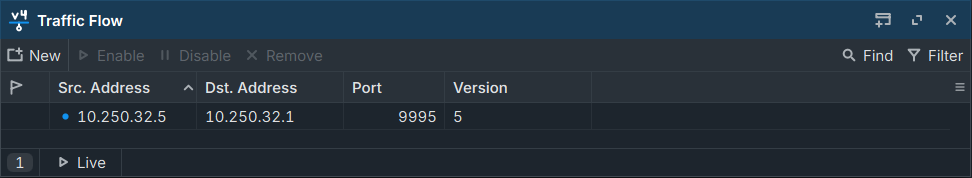
Three things decide whether it works:
/ip/dhcp-server/config/set accounting=no
/ppp/aaa/set accounting=no
# replace hsprof1 with your Hotspot server profile
/ip/hotspot/profile/set hsprof1 radius-accounting=no
In WinBox, clear the Accounting check box in IP → DHCP Server → DHCP Config and in PPP → Secrets → PPP Authentication & Accounting:
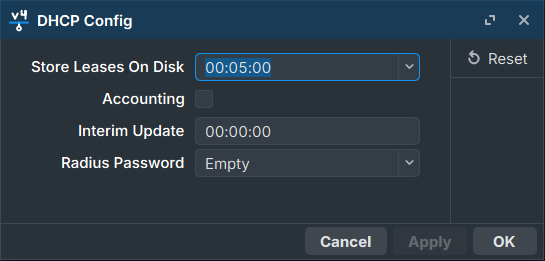
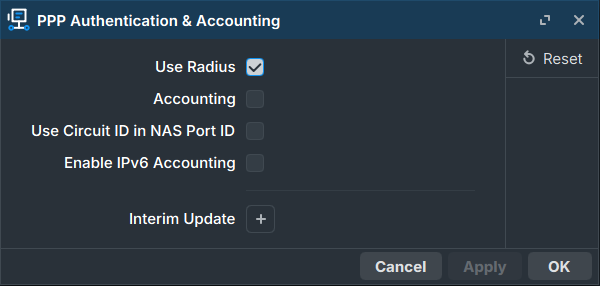
For Hotspot, clear it on the RADIUS tab of the server profile (IP → Hotspot → Server Profiles):
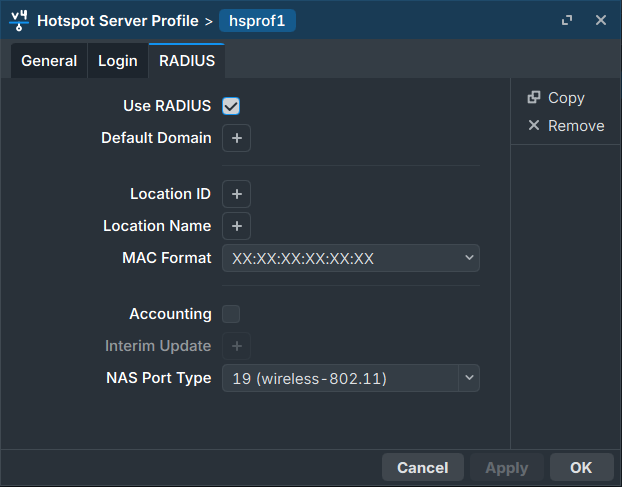
With v5, the last two sessions in a customer’s Internet statistics show no MAC address or Session ID: v5 doesn’t carry that data. If you need to leave some subnets out of the counts, Splynx traffic classes work with NetFlow accounting.
For the Splynx side (adding the router, assigning services, daemon and expiry options, and checking nfcapd when traffic doesn’t show up), see how to configure NetFlow accounting in Splynx and the NetFlow accounting documentation. If you use Splynx for RADIUS authorization on the same router, see MikroTik RADIUS configuration and troubleshooting. For everything else Splynx does for your routers, see network management in Splynx.
How to organize ISP email management: inboxes, aliases, and deliverability
A guide to setting up inboxes, email aliases, and deliverability for ISPs in Splynx. Route, send, and track every email ...
VOIP CDR Auto Processing from FTP Server
Nowadays every business is seeking to achieve the decrease of manual effort in the essential processes. Splynx voice bil...
Splynx system is a powerful set of modules and open application interfaces (API), so we call it a Framework.
Splynx's self-registration functionality allows your clients to register and helps you skip the routine process of addin...
Ubiquiti EdgeRouters PPPoE RADIUS support
UBNT EdgeRouters can act as a PPPoE server, with authentication of CPEs, providing statistics, blocking end-users, and s...
Find out how Splynx helps ISPs grow
Learn more


